
Articles from the field
Written by the people who do the work, starting from the questions we meet with clients and in our own projects.
Why is a password-cracking rig running local LLMs?
Simon shares how Bambino evolved from a password-cracking rig into PB’s local LLM environment, giving us greater control over sensitive information.

Ten years of hacking and defending
How many routes to privileged access did an attacker have in 2015, and how many are there now?
The first hour
Most organisations survive a crisis. So what does preparedness actually buy you? The difference is never survival. It is the first hour.
I did not read a book this summer
Can my organisation adopt AI without creating new security risks? This summer I stopped reading about AI and started building with it.

Do you need a CISO, but not a full-time position?
Who owns your security strategy when nobody's job title says they do? One or two days a month.
Can we crack your passwords?
Would your password policy hold if somebody actually tested it? In one engagement we recovered 67.3% of the passwords, on entirely ordinary patterns.
Unresolved risk is a transformation waiting for permission
Who in your organisation is actually allowed to fix the risks you already know about? The gap between knowing and acting is a management decision.
The illusion of resilience
When did you last question whether your security posture matches your actual risk? Most executives carry more risk than they realise, and can absorb less.
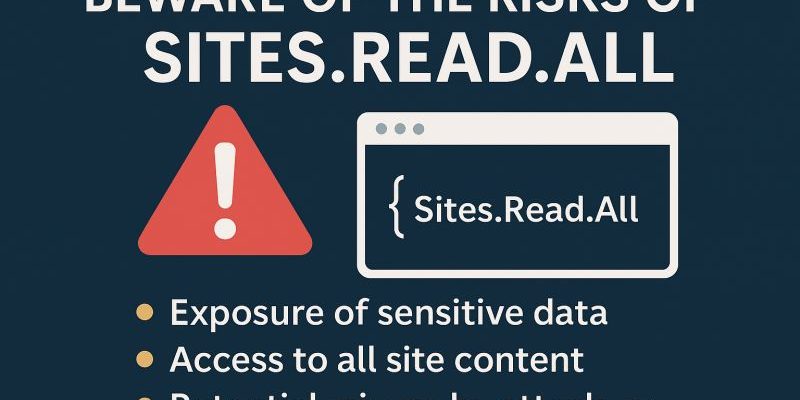
The risks of Sites.Read.All
Which applications can read every SharePoint site and every OneDrive folder in your tenant? One permission grants all of it, and it looks reasonable.

Assume Breach
If an attacker were already inside tonight, how far could they get before anyone noticed?
A CIS 18 assessment may be the wake-up call you need
You have firewalls, policies, MFA and audits. Do you know whether any of it performs in a real attack? That is not the same question as compliance.
Have you met DORA and NIS2?
Would your governance survive an audit if the regulator arrived this quarter? They have started.
Password guidance
What password policy should you actually run? Here are the lengths we recommend for users, admins and service accounts, and the work that sits beside them.
Alerting on changes to Exchange Online threat policies
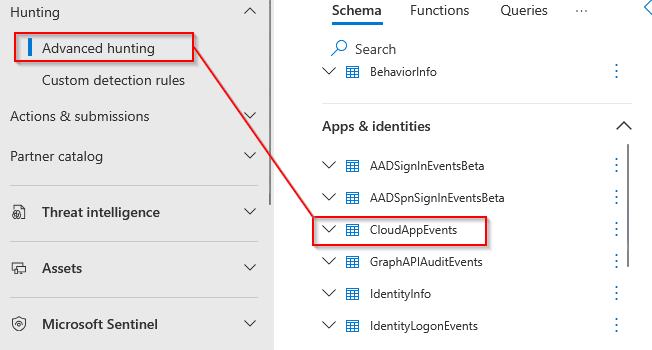
Would you know if somebody weakened your Exchange Online threat policies? The log exists, but only once you have switched the collection on.
- Why is a password-cracking rig running local LLMs?
- Ten years of hacking and defending
- The first hour
- I did not read a book this summer
- Do you need a CISO, but not a full-time position?
- Can we crack your passwords?
- Unresolved risk is a transformation waiting for permission
- The illusion of resilience
- The risks of Sites.Read.All
- Assume Breach
- A CIS 18 assessment may be the wake-up call you need
- Have you met DORA and NIS2?
- Password guidance
- Alerting on changes to Exchange Online threat policies